OSINT Jet · Suspicious-link triage
Phishing Link OSINT: Investigate a Suspicious URL Without Opening It
A suspicious link is evidence before it is a destination. Do not open it to “see what happens.” Preserve the message, separate the visible label from the real hostname, inspect public domain records and confirm the request through a channel you already trust.
Preserve the request before touching the link
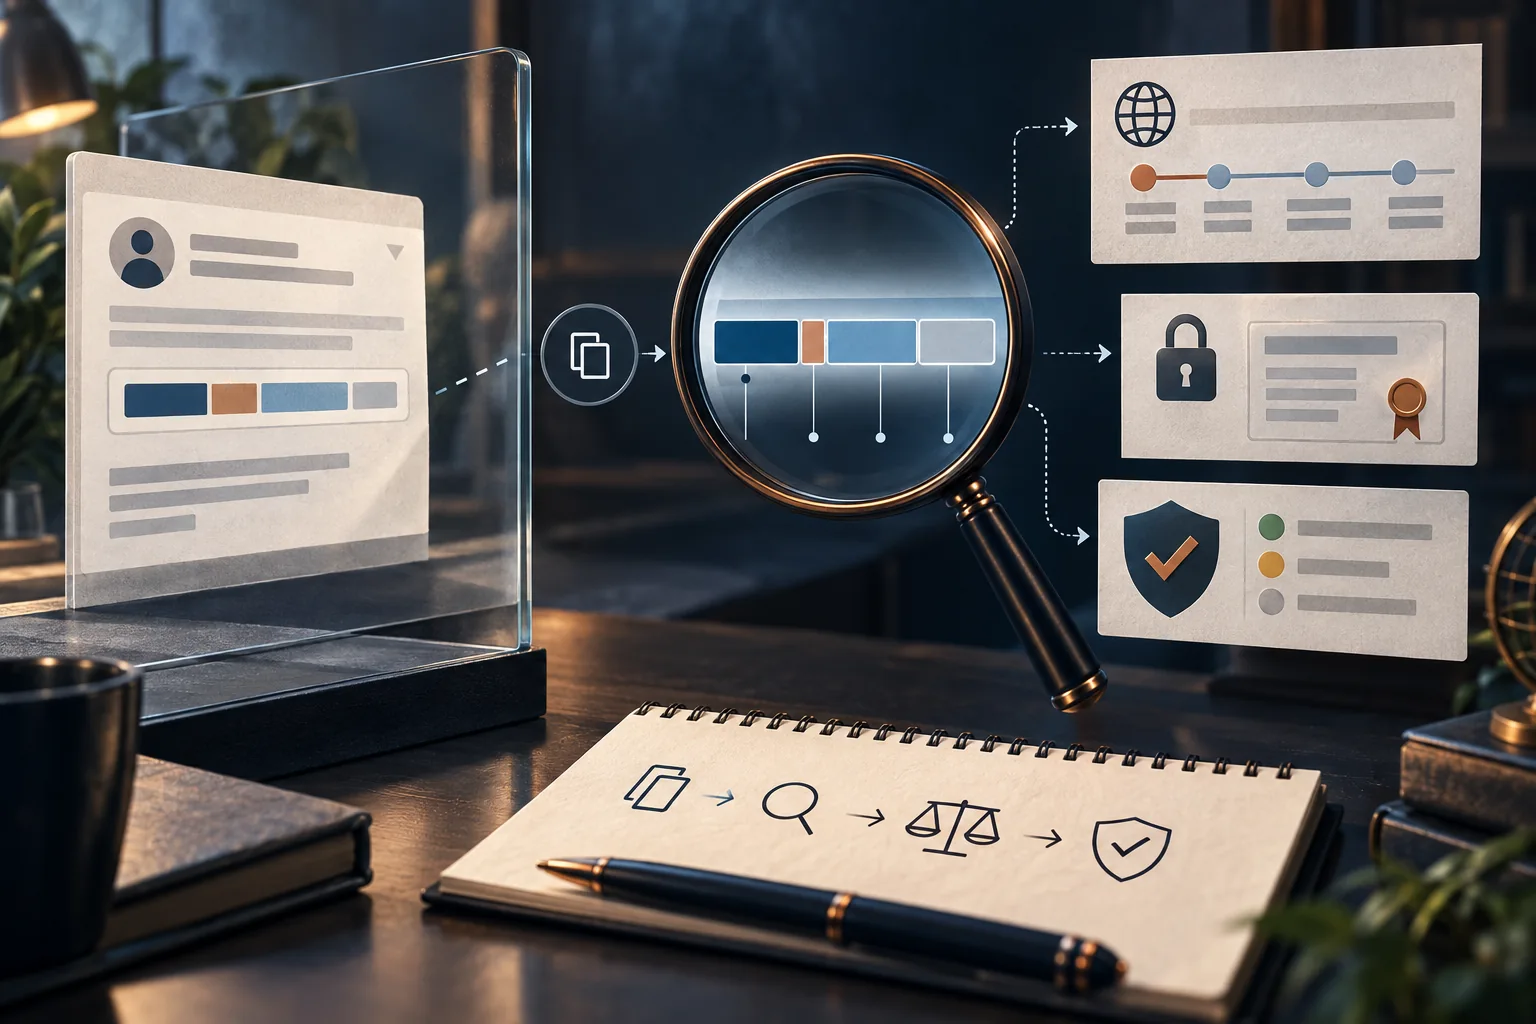
Save the full message, sender address, timestamp, subject and surrounding request. If your mail client offers “copy link address,” use it without opening the page; otherwise leave the link alone and pass the original message to your security team. Do not paste a confidential token, reset code or personalized URL into a public scanner.
CISA’s phishing tip sheet says not to click a suspicious link or attachment even when the message might be real. It recommends finding another way to contact the person or company. That is the most important step in this workflow: research supports the decision, but a known channel confirms the request.
If you already opened the link, entered a password or downloaded a file, stop treating this as a research exercise. Follow your organization’s incident process, change exposed credentials through the official site and contact the relevant provider or security team.
Read the hostname from right to left
A URL can contain a reassuring brand word almost anywhere. The registered domain is the part that controls the destination. In https://accounts.example-security.test/login, the host is accounts.example-security.test; the meaningful registrable domain may be example-security.test, not the leftmost word. A path such as /trusted-bank/ does not make the site belong to a bank.
Copy the clue into a plain-text note and mark five pieces: scheme, hostname, port if shown, path and query. Watch for a username section before @, a numeric IP address, an unexpected top-level domain, extra words around a brand, or Unicode characters that merely resemble familiar letters. Do not edit the URL into something that looks plausible; preserve the original and create a separate normalized copy for comparison.
| Observation | Useful question | What it does not prove |
|---|---|---|
| HTTPS and a lock | Is traffic encrypted to this hostname? | That the organization named in the message owns it |
| Recently registered domain | Does the timing fit the claimed service? | That every new domain is malicious |
| Brand word in a subdomain or path | What is the actual registered domain? | Affiliation with that brand |
| No warning in a reputation tool | Was this URL observed by that service? | That the page is safe or legitimate |
Use public records as context, not as a safety certificate
Look up only the hostname or registrable domain, not a private query string. ICANN Lookup uses RDAP to retrieve current registration data from registries or registrars. Note the creation date, registrar, status and nameservers when present. Privacy-redacted registrant data is normal; it is not a malicious indicator.
Compare the domain with the organization’s official site found independently—not through the message. Does the official help page mention the same domain? Do known emails and support links use it? The Google Safe Browsing status tool can show whether Google currently identifies a site as dangerous. A “no data” or clean result is not approval: new, low-volume or compromised pages can escape a snapshot.
For DNS and RDAP interpretation, use the domain OSINT guide. Registration age, hosting and certificates are supporting signals. None answers whether the specific request in your inbox is authorized.
Fictional case: an invoice portal with one extra word
This example is invented. A message says a supplier moved invoices from northharbor.example to northharbor-billing.example and asks the recipient to sign in before lunch. The visible button says “Open supplier portal.” Copying the link reveals a personalized path on the second domain. RDAP shows the second domain was created two days earlier. The supplier’s independently found website has no migration notice, and its known finance phone number confirms that the portal has not changed.
The strongest finding is not “two-day-old domains are phishing.” It is: the request uses a newly created, different domain and contradicts confirmation through the supplier’s known official channel. Preserve the message, report it through the mail provider or organization process and do not visit the page. The personalized path remains private; it does not need to be shared with a public lookup service.
If the finance contact had confirmed the change, the new registration date would become an explained fact rather than a verdict. That is why the verification channel matters more than a pile of red-flag scores.
A safe-looking domain can still host a bad request
A legitimate site can be compromised, a third-party campaign platform can be authorized, and a familiar domain can contain an unsafe user-generated page. Conversely, a small organization may legitimately use a new domain. Record what each check saw and the observation time. Avoid labels such as “100% safe” or “confirmed malicious” unless the evidence and responsible authority support them.
The broader scam OSINT guide helps break a suspicious message into claims. This page owns the narrower, no-click link triage. For email authentication and sender/domain separation, use the email OSINT guide.
Finish with one proportionate action
Your note should contain the exact request, preserved URL, parsed registered domain, relevant public records, the trusted confirmation channel and the decision. Delete or redact unnecessary tokens before sharing the note. Report the message through the official platform or security route; do not confront the sender or explore the page from a personal device.
For a single obvious mismatch, these free checks may be enough. When a suspicious request links an email, domain, company claim and reused image, OSINT Jet can organize the public clues and uncertainty into a report someone else can review. It does not visit private systems or certify a site as safe. Use the report template for your own case, or review current report options when the decision needs a documented investigation.
Published by OSINT Jet · Original publication: 29 September 2026